
A new phishing campaign targets advertising account managers. The operation uses fake sites for ChatGPT, Gemini, Claude, and Perplexity to steal login credentials and multi-factor authentication codes.
Researchers discovered the phishing operation leveraged the recent launch of the Muse AI agent. Meta describes this agent as an assistant for various personal tasks.
Fake AI tools harvest credentials
The malicious pages target agency staff, media buyers, and administrators. These users manage accounts that extend to multiple downstream clients. Attackers can spend available balances on fraudulent ad campaigns or resell compromised accounts to other cybercriminals for significant amounts.
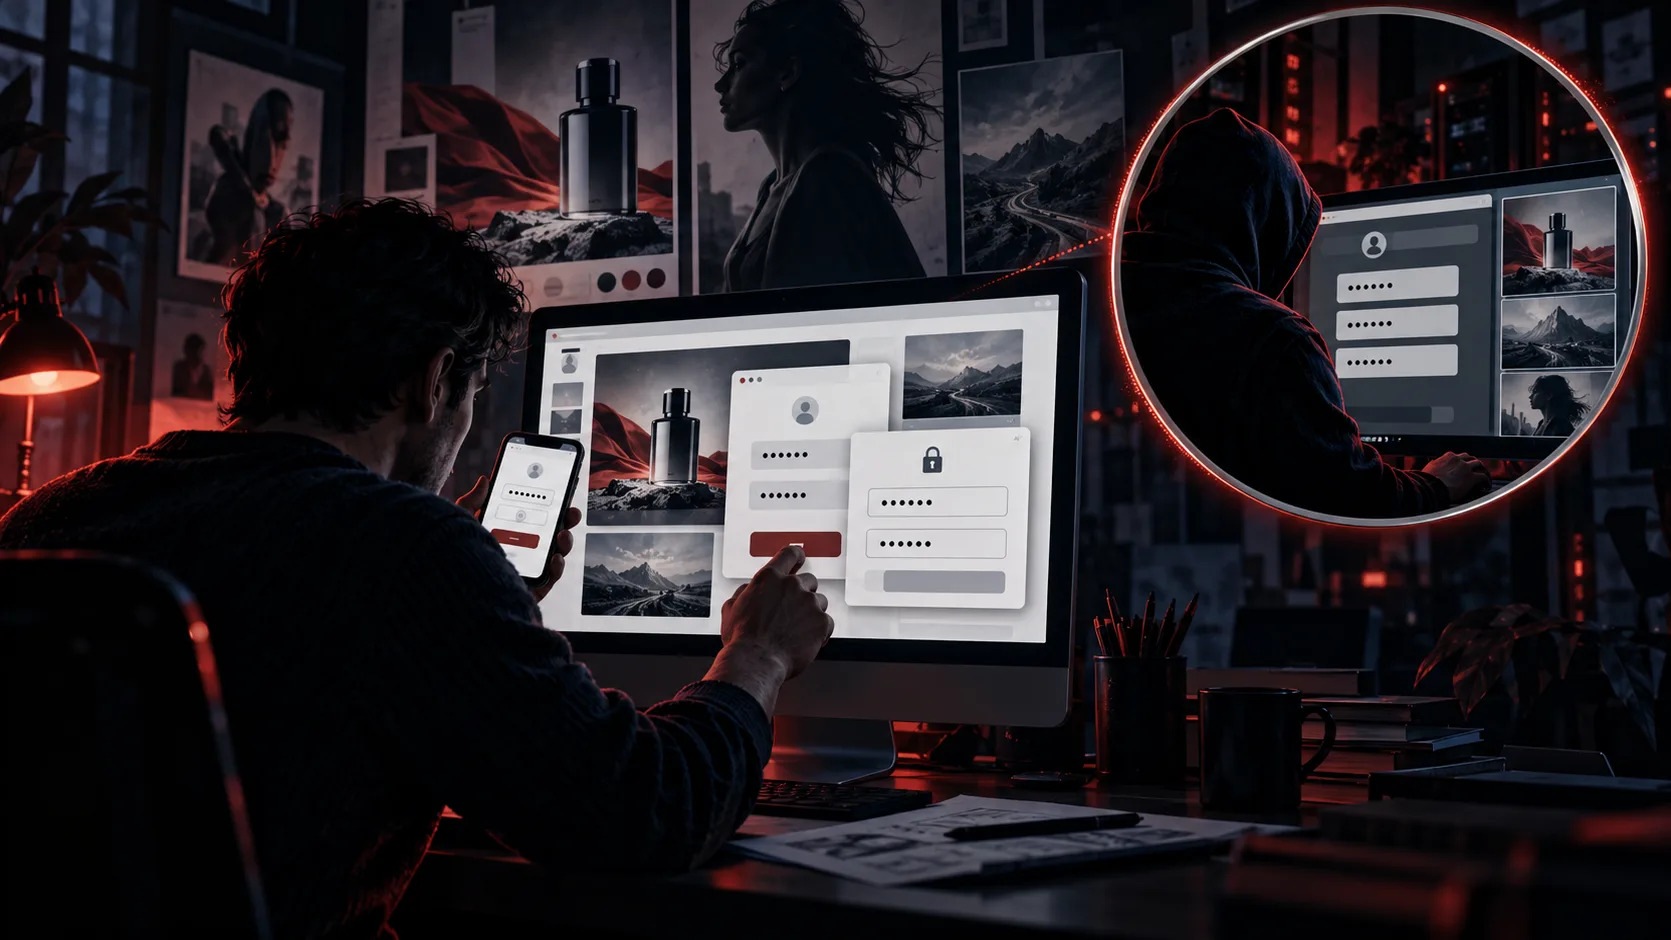
Phishing sites claim to help advertisers reach buyers, obtain ad briefs, and plan advertising campaigns. Users must connect their accounts to the fake AI product to receive these benefits. Clicking the connect button opens a fake Google window inside the page with a realistic address bar.
Browser-in-the-browser attacks deceive users
This method is known as a browser-in-the-browser attack. Cybersecurity researcher mr. dox devised the phishing technique in March 2022. It creates a fake browser window inside a legitimate one to display a fraudulent login page.
The fake window is an iframe featuring realistic titles, interfaces, and expected login URLs. Researchers at browser security company Island report that an attacker uses a kit adapting the interface to Windows, macOS, iOS, and Android. A human operator then takes over to control prompts.
 Read nextDeepseek Eyes $15 Billion Funding Round And 2027 IPO
Operators control the phishing flow
Attackers may ask for password entries up to three times. They can request SMS or authenticator codes, display Okta push requests, show Google approval prompts, or present QR codes. Operators can reject submitted codes and hold victims in a waiting screen.
Investigators found this campaign links to a larger operation using fake recruitment and refund lures. All pages share a Next.js and Socket.IO stack with common API endpoints. The connection was traced because the attacker exposed older source code through misconfigured public GitHub repositories.
Researchers found the Telegram control channel used in the attacks received hundreds of victim submissions. The phishing platform supports Google, Meta, TikTok, and Okta sign-in workflows. Island researchers published a list of dozens of URLs associated with this activity.